Co-Management
The customer shouldn’t have to wait, but there are still configs MSPs want their engineers to own.
A URL exception. A user lookup. A scheduled report. The customer does those without opening a case, and without the keys to the whole tenant. SSL inspection, the baseline policy, and admin rights stay with the MSP.
You see the edit in the same record as your own work. If it was wrong, you put the config back. The log of that edit is immutable: who, what, when, and from where, whether it was your engineer or the customer. You cannot rewrite it.
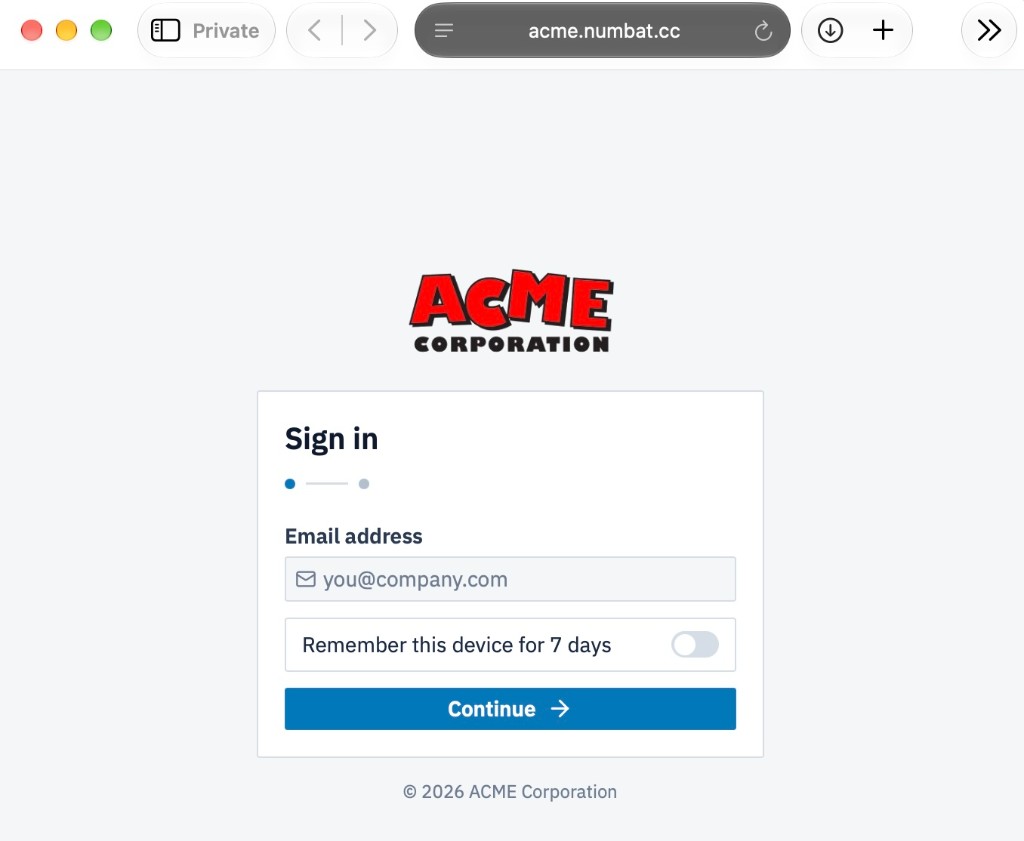
Co-management is whitelabelled. The customer signs in on your hostname, under your logo. NUMBAT is not on that screen. The reports they receive, compliance and traffic, export as your PDF.
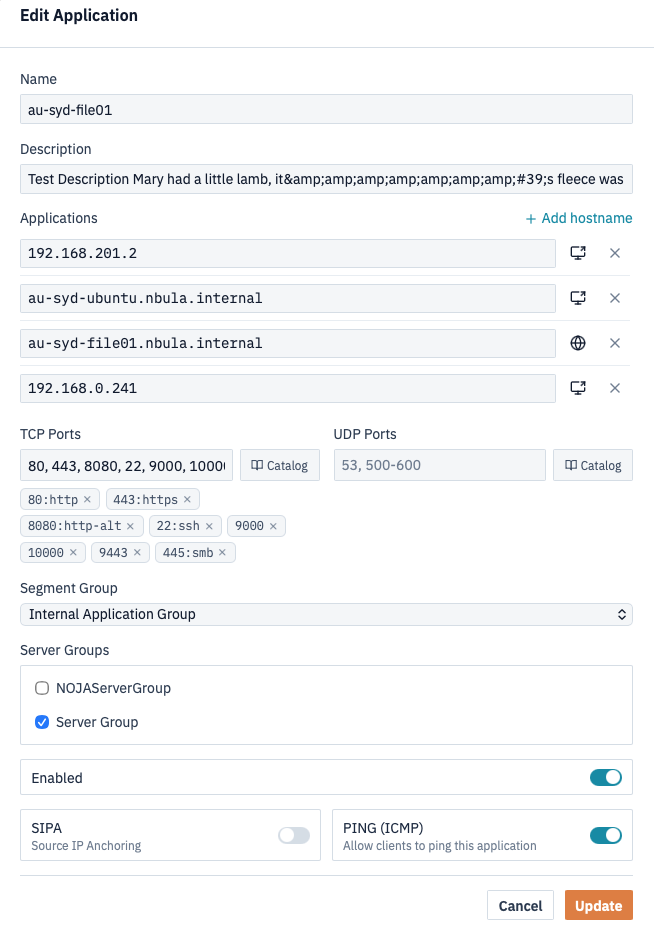
Scoped access, not a shared admin login. The customer can touch the objects you allow, and nothing past them.
Immutable logging covers both sides of the split. A customer change and an engineer change land in the same ledger, and neither can be edited out later.
Broad rights feel faster until an emergency edit lands in the wrong tenant. The slower setup is the one you can defend.
Global Information Technology Director, Trajan Scientific and Medical
We chose a co-management strategy with our MSP. NUMBAT enabled us to make the simple changes safely without cases opened. We now only engage the MSP for the issues that are complex. We can also see who made any change and reverse it in seconds.
Your brand. Their everyday change.