Get answers in seconds, without waiting on Zscaler logging.
The ticket is already open. The delay is not a lack of logs. It is the time spent finding the right tenant, the right user, and the control that made the decision. Policy, authentication, SSL inspection, application control, or a category. Those are different answers, and only one of them is the fix.
The native console can show the block, if you are already in that tenant and you wait for it. It will not put the event next to the rule, or tell you the rule was edited on Tuesday.
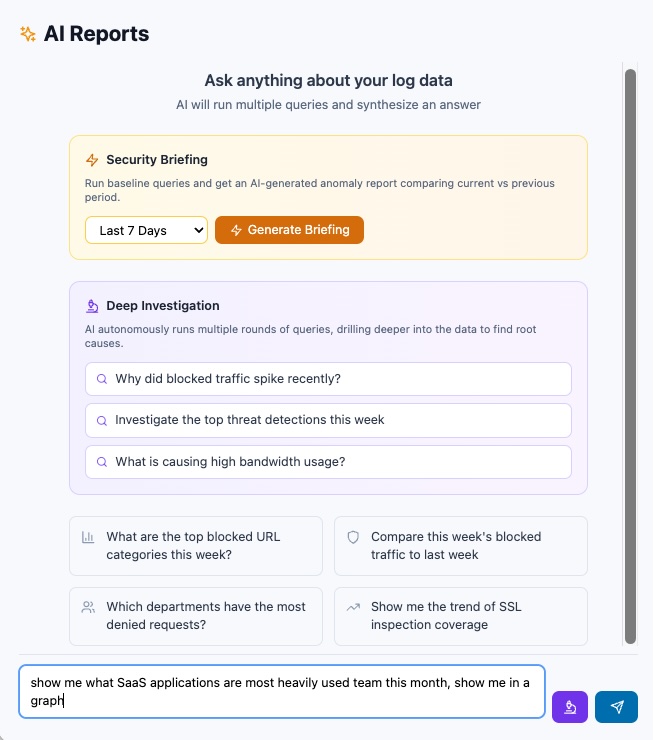
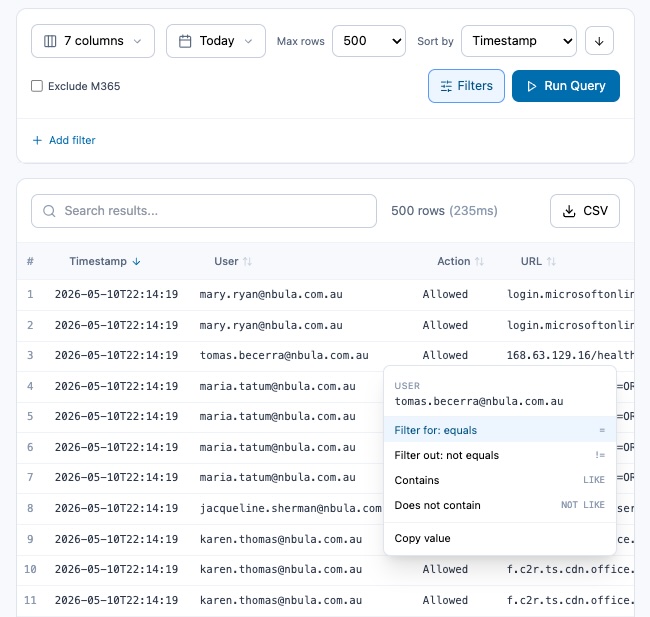
The block. The rule that matched. Whether anyone changed that rule this week. Pick a user, a URL, a category and a time. A 90-day slice comes back in seconds. Up to 13 months of the NSS feed stays hot, on our own hardware.
If the block was expected, close the ticket with the rule name. If it was not, change the narrow thing. A broad allow restores access and leaves a hole the next ticket will not mention.
Each customer has their own users, names and exceptions. Searching the tenant next door wastes the hour and can put the exception in the wrong place.
The same block in three tenants is a standard that is wrong, not three one-off tickets. One search should show whether it is isolated or repeated.
Senior engineers end up as the only people who know where to look. The log question should not depend on who is on the rota.
Ask it of your own logs.
30 day demo